What is Shadow AI? The Hidden Security Risks in Your Tech Stack
Introduction
AI tools are becoming common in everyday business tasks. However, unapproved AI use can create hidden security risks. This guide explains Shadow AI, its risks, and ways businesses can manage it safely.
What Is Shadow AI?
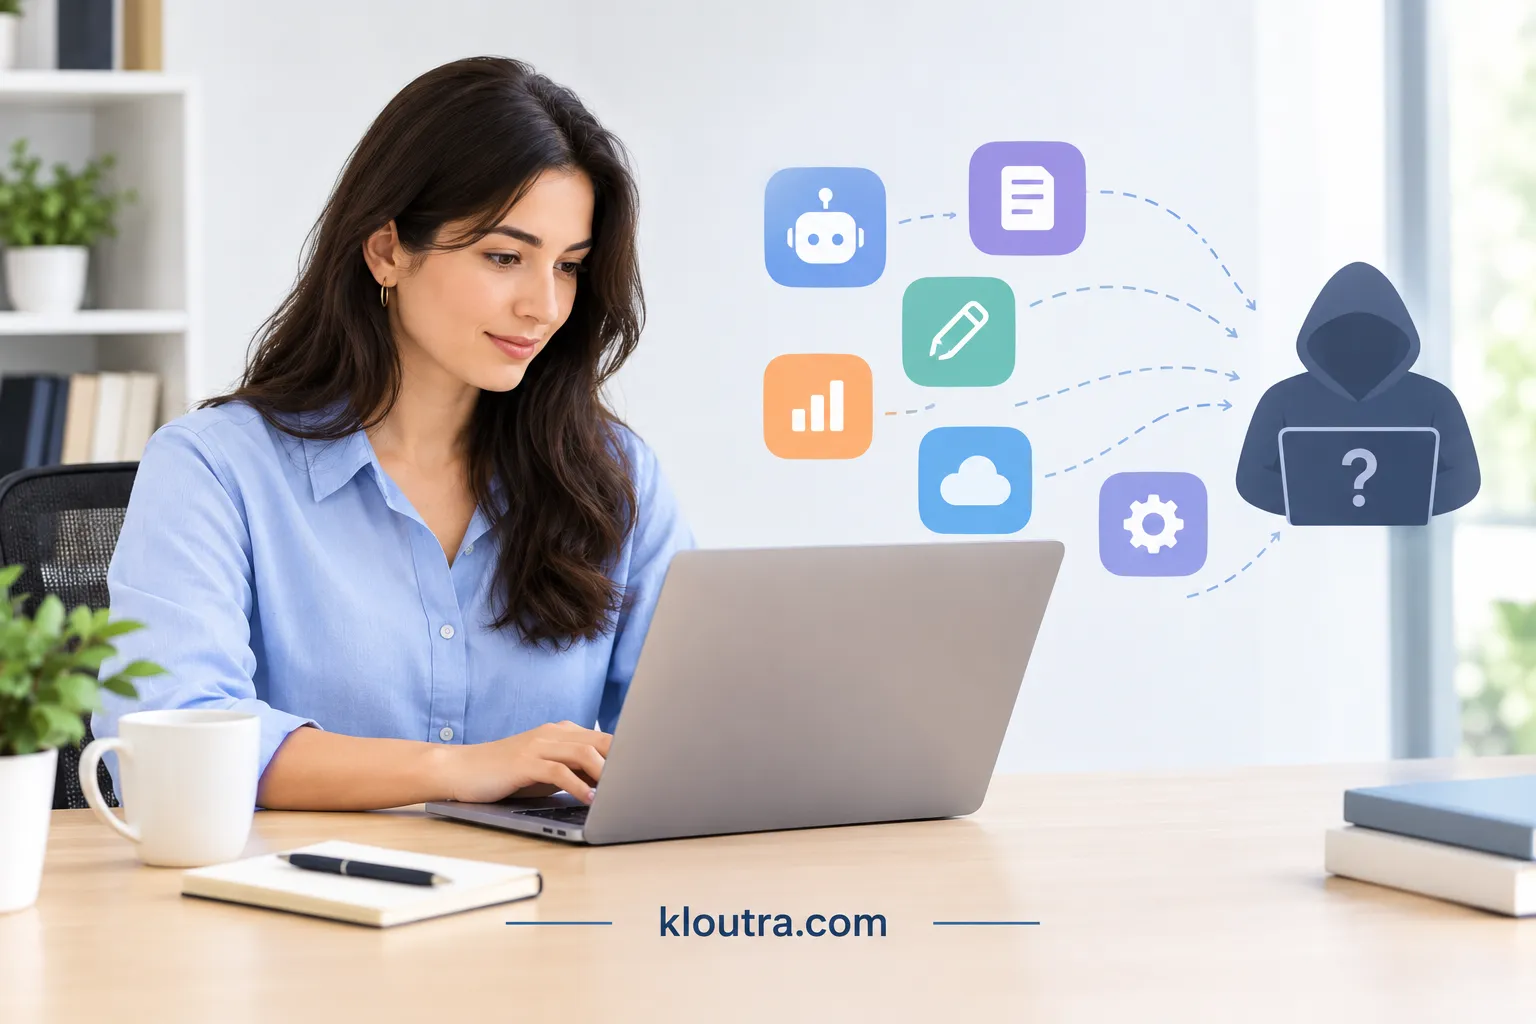
Shadow AI is when employees use AI tools without their company’s approval. These tools may include chatbots, writing assistants, or AI-powered software.
The main risk comes from using AI without proper security measures. Employees may share sensitive business information with external AI tools. This can lead to privacy, security, and compliance problems.
Shadow AI can also exist inside approved software through built-in AI features.
In simple terms, Shadow AI is unmanaged AI use within an organization.
How Shadow AI Enters a Company’s Tech Stack
Shadow AI can enter through personal tools or AI features already built into business software. These tools may be used without involving IT or security teams.
Employees Using Unapproved AI Tools
Employees may use public AI tools for everyday work tasks. They might summarize documents, write emails, analyze data, or create content.
Problems arise when employees use personal accounts for company work. Sensitive company information can then reach an unapproved external service.
AI Features Hidden Inside Everyday Software
Shadow AI does not always involve a new application. Many existing business tools now include built-in AI features.
These features can process company data without appearing as separate AI applications. This can make them harder for security teams to identify and manage.
Why Employees Turn to Shadow AI
Employees often use Shadow AI because it helps them finish tasks faster. AI can summarize information, draft content, analyze data, and handle repetitive work.
Some employees also find approved AI tools limited or difficult to use. When company options do not meet their needs, employees may choose familiar alternatives.
Easy access also makes Shadow AI simple to adopt. Many AI tools are available online without requiring company approval. In some cases, employees simply do not understand the security risks. Clear AI policies and training can help reduce unsafe usage.
Shadow AI vs. Approved AI: What’s the Difference?
| Feature | Shadow AI | Approved AI |
|---|---|---|
| Company approval | Used without official company approval. | Approved and managed by the organization. |
| Security review | May not receive a formal security review. | Usually reviewed under company security requirements. |
| Data protection | Data handling may be unclear to the company. | Data handling follows defined company policies. |
| Visibility | IT teams may not know the tool is being used. | IT teams can track and manage its use. |
| Access controls | May operate outside company access controls. | Uses company-defined access and security controls. |
| Governance | Often falls outside AI governance processes. | Operates under established AI governance policies. |
| Risk management | Risks may remain unidentified or unmanaged. | The organization can assess and manage identified risks. |
Approved AI does not mean the tool has zero risk. Organizations still need policies, monitoring, and ongoing risk management.
The Hidden Security Risks of Shadow AI
Shadow AI can create security problems when employees use AI without company controls. The risks can affect data, accounts, content, vendors, and privacy.
Sensitive Data Exposure
Employees may enter confidential information into unapproved AI tools. This can include customer details, company data, or internal documents. CISA recommends avoiding sensitive information in public AI tools.
Intellectual Property and Confidentiality Risks
Employees may share source code, designs, research, or other protected material. This can create intellectual property and confidentiality concerns for businesses.
Account and Access Control Problems
Unapproved AI tools may use personal accounts instead of company accounts. This can make access harder to manage and monitor. AI systems with broad access can also create additional security risks.
Inaccurate or Unsafe AI-Generated Content
AI tools can produce incorrect or misleading information. Employees may use that content without checking it first. CISA recommends treating AI as a helpful tool, not a replacement for expertise.
Third-Party AI Vendor Risks
External AI services can create privacy and security risks. Companies may not know exactly how these services store or use their data. NIST recommends assessing third-party AI providers and their security practices.
Compliance and Data Privacy Concerns
Shadow AI can make it harder to follow privacy and security requirements. Unapproved tools may handle personal or sensitive information without proper monitoring. Organizations need clear policies for managing AI-related privacy risks.
Which Business Data Is Most at Risk?
Some business data needs stronger protection when employees use AI tools. This includes confidential, personal, and proprietary information.
Customer information can include names, contact details, and other personal data. Employees should avoid entering this information into unapproved AI tools.
Financial records, business plans, and internal reports can also face exposure. These details may reveal sensitive information about company operations.
Source code, product designs, and research can contain valuable intellectual property. Sharing them with unapproved AI tools can cause security risks.
Passwords, API keys, and access credentials also require strong protection. Employees should never enter these secrets into AI tools.
Companies should classify sensitive data before allowing employees to use AI. This helps teams apply suitable controls and reduce data exposure risks.
Real-World Examples of Shadow AI in the Workplace
Employees may use public AI tools to write emails, summarize documents, or create content. They may also upload company information without checking approval or security rules.
Developers might use unapproved AI coding tools with company source code. Employees may also use AI features inside business software without security teams tracking them. These examples show how AI can enter workplaces without proper oversight.
How to Detect Shadow AI Across Your Organization
Monitor AI Tool Usage
Keep track of the AI tools employees use for work tasks. Regular monitoring helps security teams find unapproved AI usage.
Review SaaS and Browser Activity
Review SaaS applications and browser activity for unknown AI services. This can reveal AI tools outside approved company systems.
Identify Unusual Data Transfers
Watch for unusual data transfers to external AI services. Large or unexpected transfers may need further security review.
How Businesses Can Reduce Shadow AI Risks
Create a Clear AI Use Policy
Start with simple rules that explain which AI tools employees can use. Also, clearly define what company data employees must never share.
Provide Approved AI Tools
Give employees secure AI tools that meet company requirements. This way, employees have safer options for everyday tasks.
Apply Data Loss Prevention Controls
Security controls can help prevent sensitive data from leaving company systems. In addition, they can reduce accidental data exposure.
Train Employees on Safe AI Use
Regular training teaches employees how to use AI tools safely. For example, explain data risks, approved tools, and common security mistakes.
Review AI Vendors and Integrations
Before connecting an AI service, review its security and privacy practices. Also, check how the vendor handles data, access, and integrations.
How to Build a Safer AI Governance Strategy
Start by creating clear rules for how employees can use AI. Assign specific teams to manage AI risks and responsibilities.
Keep an inventory of the AI tools used across the organization. Review these tools regularly as business needs and risks change.
Assess AI systems before employees use them with sensitive data. Check security, privacy, access controls, and vendor practices. Monitor AI systems after deployment for new risks. Regular reviews can help organizations detect problems and update controls.
Finally, document AI decisions, incidents, and important risk assessments. This creates clearer accountability and supports consistent AI risk management.
What the Future of Shadow AI Looks Like
As AI use grows, companies will need better visibility across their AI tools. Businesses will create clearer rules for approved AI use. Employees will also receive more training on safe AI practices.
Finally, companies will review AI risks throughout the system lifecycle.
Final Takeaway: Making AI Use More Visible and Secure
Shadow AI creates risks when companies cannot see how AI is being used. When employees use unapproved tools, sensitive data may leave the company unnoticed.
The answer is not to block AI completely. Instead, companies should make AI use clear and controlled. Clear policies, approved tools, and basic employee training can help reduce these risks.
Shadow AI will not disappear by itself. However, better visibility and security controls can help businesses use AI more safely.
Disclaimer:
This article provides general information about Shadow AI and AI security risks. It is not a substitute for professional cybersecurity, legal, or compliance advice. Always review your organization’s specific security policies and requirements.

Related Posts
Mobile App Development Tips for Beginners
Best Spotify Alternatives for Music Streaming